JYS Cyber Assurance helps venture- and PE-backed companies place the coverage that matters most at critical growth stages—Cyber Liability, Tech E&O, D&O, and AI Liability. We also place the full range of commercial property & casualty coverage—General Liability, Business Owners Policies, Workers' Comp, Umbrella, and more—so every policy stays under one roof as your business grows.
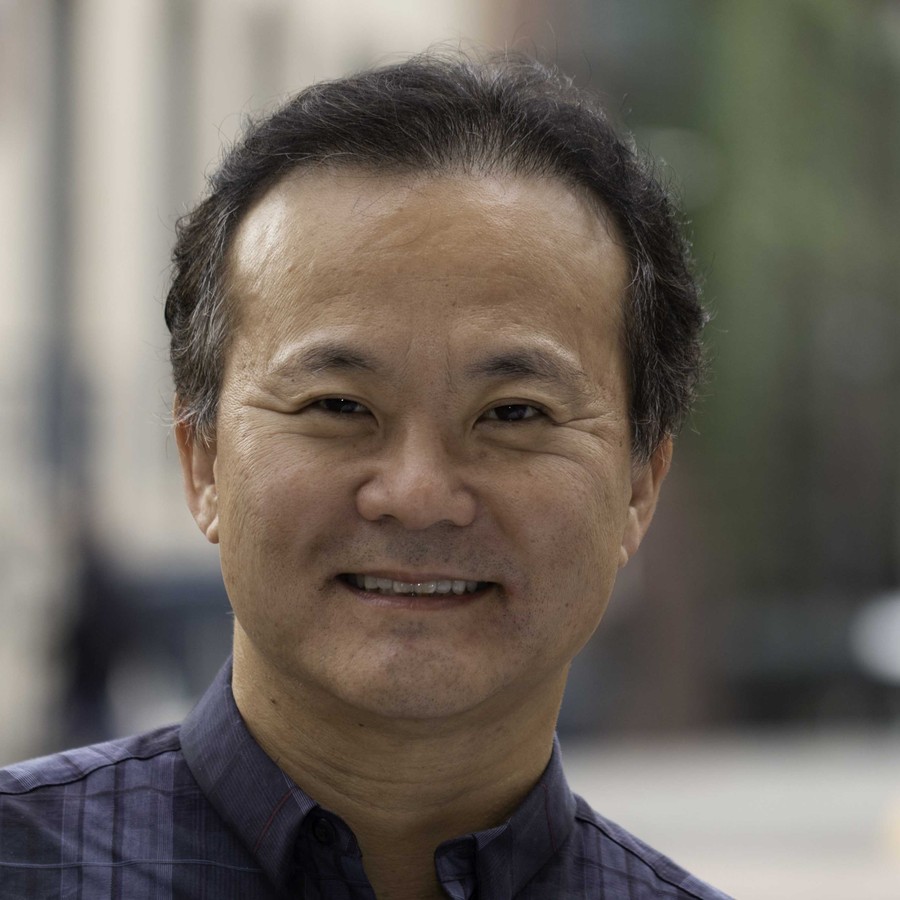
Founder John Song spent thirty years building and selling companies before doing this—including a NASDAQ IPO, three exits, and nearly nine years running an AI company—and knows this business from the buyer's side of the table. Read his story →
Let's start a conversationI look at policies through the lens of a founder managing cash flow and risk, not a broker hitting a sales target.
I understand what corporate security teams look for before they sign off on a contract.
I ran an AI company for nearly nine years. I know how fast model risk and AI liability can move, because I managed it from the inside.

I was part of the founding team at ARIS, where we took the company from a basement startup to a NASDAQ IPO with over $115 million in revenue, completing eight acquisitions along the way. Since then, I've started, scaled, sold, and occasionally wound down several other ventures—most recently TenPoint7, an AI firm I led for nearly nine years. In 2024, when LLMs reshaped the landscape, I made the conscious decision to close it down. Evaluating risk and knowing when to pivot or exit is simply part of the entrepreneurial life cycle.
That decision is also why AI liability isn't theoretical for me. I watched the insurance market scramble to keep up with generative AI in real time—coverage that used to sit quietly, unnamed, inside a standard cyber or tech E&O policy is now being explicitly written in or carved out, and companies building on LLMs or AI agents are often the last to find out which one applies to them. It's a conversation I have with founders regularly now.
One experience shaped how I view risk more than any other. As CEO of a startup doing under $3M in revenue, I had to guide us through a national bank's 140-point vendor security audit. It was uncomfortable, but it forced me to address operational risks I hadn't taken seriously enough until a large customer made me.
That is the perspective I bring to this work. I may be newer to the insurance industry, but I am not new to risk. I've raised capital, managed cloud migrations, closed M&A deals, and made payroll.
If you're building a company and want a sound board who understands the journey, let's connect.
Four specific milestones usually drive our best work together:
When your product starts collecting customer, financial, or health data, your exposure changes fast.
If your product uses generative AI, LLM-generated outputs, or AI agents that take action inside your systems or a customer's, your risk profile just changed—and it's likely your current policy was never written with that in mind.
New investors bring more stringent formal governance expectations. That usually means higher board oversight and increased insurance requirements.
Their procurement team is going to send a security questionnaire you haven't had to answer before. I've sat on your side of that table.
| Coverage | Why It Matters at Your Stage |
|---|---|
| Cyber Liability | Covers data breaches, ransomware, wire fraud, and business downtime. If you handle customer data, this is mandatory to protect your runway—and it takes more than a cyber endorsement bolted onto your general liability policy. You need a dedicated policy built for these exposures. |
| Tech E&O | Protects against claims that software bugs, outages, or services caused client financial loss. Enterprise procurement teams will ask for this immediately. |
| AI Liability | Fills the gap standard cyber and tech E&O were never written for—model errors and hallucinations, IP or defamation claims from AI-generated content, and liability from AI agents acting inside your systems or a customer's. It's the fastest-moving corner of the market right now, and most founders haven't reviewed whether they're actually covered. |
| Directors & Officers (D&O) | Protects founders and board members personally from management lawsuits. Essential as soon as you take outside capital. |
| General Commercial P&C | General Liability, Business Owners Policies (BOP), Workers' Comp, and Umbrella round out your foundational coverage—all under one roof, so nothing falls through the cracks at renewal time. |
Generative AI-related lawsuits in the US grew 978% between 2021 and 2025, and most insurance policies still handle AI liability as an afterthought tucked inside existing cyber and tech E&O coverage. Carriers are starting to notice the gap—and starting to exclude it outright.
When a national bank handed us a 140-point vendor security audit, my initial reaction was concern. We were a lean team without a dedicated security officer. But going through the audit turned out to be a huge help. It forced us to establish clean rules around data access, device safety, and incident management.
If you want to review your current coverage, understand how AI liability fits into your existing policies, prepare for an upcoming security audit, or simply exchange notes founder-to-founder, reach out directly.
Whether you're six months from a Series A or staring down your first enterprise security questionnaire, I'm glad to talk it through—no pressure, no sales script.
Disclosure: Insurance offered through John Song, a licensed producer in Washington State. This site is for informational purposes and does not constitute an offer of coverage.